Events and audit
Events: ISuperAdminEvents
Implement only the methods you need and register the class. You may register several handlers.
- Handlers run after the change is saved.
- An exception in a handler is logged. It does not undo the change.
public sealed class AuditEvents(MyDbContext db) : ISuperAdminEvents
{
    public async Task SignInFailedAsync(SignInFailedEvent e, CancellationToken ct)
    {
        db.AdminAuditLog.Add(new() { Action = "login-failed", UserName = e.UserName, Detail = e.Reason.ToString(), Ip = e.Ip, At = e.At });
        await db.SaveChangesAsync(ct);
    }

    public async Task UserChangedAsync(UserChangedEvent e, CancellationToken ct) { /* Created, Updated, Deleted, PasswordChanged, ... */ }
}

builder.Services.AddScoped<ISuperAdminEvents, AuditEvents>();
| Method | Raised when |
|---|---|
SignedInAsync | A user signs in |
SignInFailedAsync | A sign-in fails. The reason is one of: unknown user, wrong password, locked out, inactive, rate limited |
SignedOutAsync | A user signs out |
UserChangedAsync | A user is created, updated, deleted, changes password, ... |
RoleChangedAsync | A role changes |
PermissionChangedAsync | A permission or its URL rules change |
MenuChangedAsync | A menu item changes |
Each event carries the acting user (Actor) and the time.
Operation log sinks: IOperationLogSink
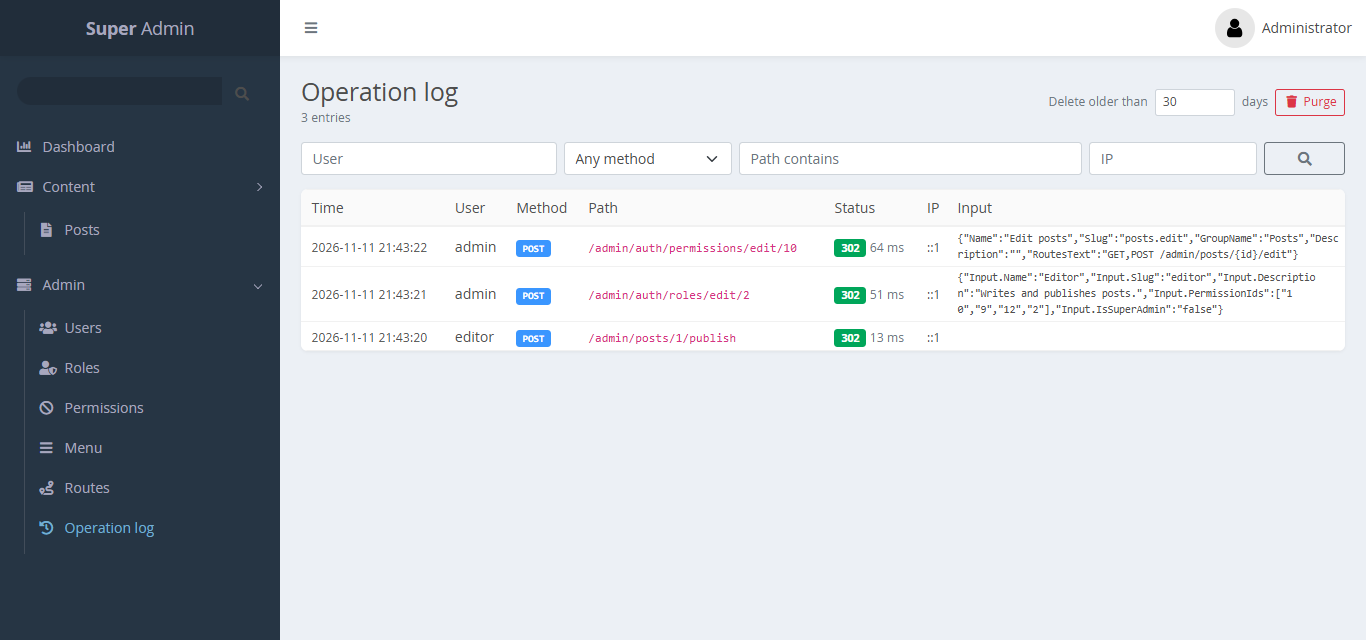
The operation log records write requests with redacted input. It can go to your own table too. Sinks are additive.
public sealed class AuditSink(MyDbContext db) : IOperationLogSink
{
    public async Task WriteAsync(IReadOnlyList<SaOperationLog> entries, CancellationToken ct)
    {
        db.AdminAuditLog.AddRange(entries.Select(e => new AdminAuditLog { Action = e.Method + " " + e.Path, UserName = e.UserName, Detail = e.Input, At = e.CreatedAt }));
        await db.SaveChangesAsync(ct);
    }
}

builder.Services.AddScoped<IOperationLogSink, AuditSink>();
To send entries only to your sink, turn off the built-in table with OperationLog:WriteToDatabase = false.
What the operation log records
| Key | Default | Meaning |
|---|---|---|
OperationLog:Enabled | true | |
OperationLog:Methods | POST, PUT, PATCH, DELETE | Methods that are logged |
OperationLog:Except | [] | Patterns never logged. The log page itself is always excluded |
OperationLog:RedactKeys | [] | Extra keys to mask. password, secret, token, apikey and authorization are always masked, recursively in form and JSON bodies |
OperationLog:MaxBodyBytes | 65536 | |
OperationLog:RetentionDays | 90 | Older entries are removed |